Protecting client information starts with the right next step. I help tax, accounting and healthcare offices review their risks, strengthen everyday security, and put a clear plan in place.
Multi-factor sign-in on email, banking and business software.
Email authentication settings: SPF, DKIM and DMARC.
Your backups, including an agreed restore test.
Encryption and updates on the devices in scope.
You leave with a prioritized fix list.
Your one-page priorities and supporting findings arrive within five business days after the review and receipt of the required information and access. A 30-minute call explains your next steps.
This is a focused assessment, not a full compliance risk analysis. We agree the accounts, devices and feasible restore test before booking; configuration work is separate. If you move to a larger engagement, reusable assessment work is reflected in your written quote.
A connected view of your office
Find the gaps between your tools.
A review looks at how your accounts, devices and recovery plans work together.
AccountsSign-in & access
DevicesEncryption & updates
Your officeOne clear review
RecoveryBackups & restore
Your planPriorities & ownership
Illustrative review framework · Findings depend on your environment and agreed scope.
02 / Tax & accounting
Tax Office WISP & Security Review
From $1,750
For solo preparers and offices with up to 5 staff
Turn your written information security plan into a practical guide for protecting your clients and running your office.
A tailored WISP based on your actual systems, responsibilities and practices, informed by IRS guidance and the FTC Safeguards Rule.
A review of accounts, devices, backups and information handling, with prioritized gaps and assigned next steps.
An incident-response checklist covering escalation contacts and reporting considerations.
A walkthrough of the plan and your office’s ongoing responsibilities.
50% at signing, 50% at delivery. Configuration work is separately scoped. Your written agreement confirms systems, deliverables and timing; this is not a compliance certification.
For practices with 1–3 providers, subject to scope
Understand the risks to electronic patient information and leave with a documented, prioritized plan.
Map where your practice creates, receives, maintains and transmits electronic protected health information.
Assess administrative, physical and technical safeguards, threats and vulnerabilities across the agreed environment.
Document findings, risk priorities, recommended actions and responsible owners.
A remediation roadmap with planning-level cost ranges and a findings walkthrough.
50% at signing, 50% at delivery. We qualify your systems and information flows before quoting. Implementation and third-party services are separate; cost ranges are estimates, not vendor quotes or a certification.
Keep an established security plan current, with scheduled reviews and practical guidance for your team.
Quarterly reviews of agreed security priorities and changes to your office.
One scheduled annual review of your existing WISP or risk-analysis documentation, with routine updates.
One remote staff security-awareness session, up to 60 minutes, per 12 months of service.
Routine account/access assistance within your agreed support allowance; email replies within two business days.
Three-month minimum: $1,125 total, billed at $375/month. Your agreement sets support allowances and the annual review/training schedule. Major changes, new risk analyses, monitoring and incident response are separately scoped. Renewal and cancellation terms are agreed before enrollment.
Prices shown in USD. Starting prices apply to typical small offices; larger or more complex environments receive a tailored quote. Your written scope confirms the total, delivery schedule, included work and any separate software or travel costs before you commit.
Custom apps / Small business operations
Software that works the way you do.
Custom apps for small businesses that bring inventory, checkout and everyday operations together—built around your workflow, your team and the way you sell.
Built by DanieleLabs / Starmarked Studio
See the work. Picture what’s possible.
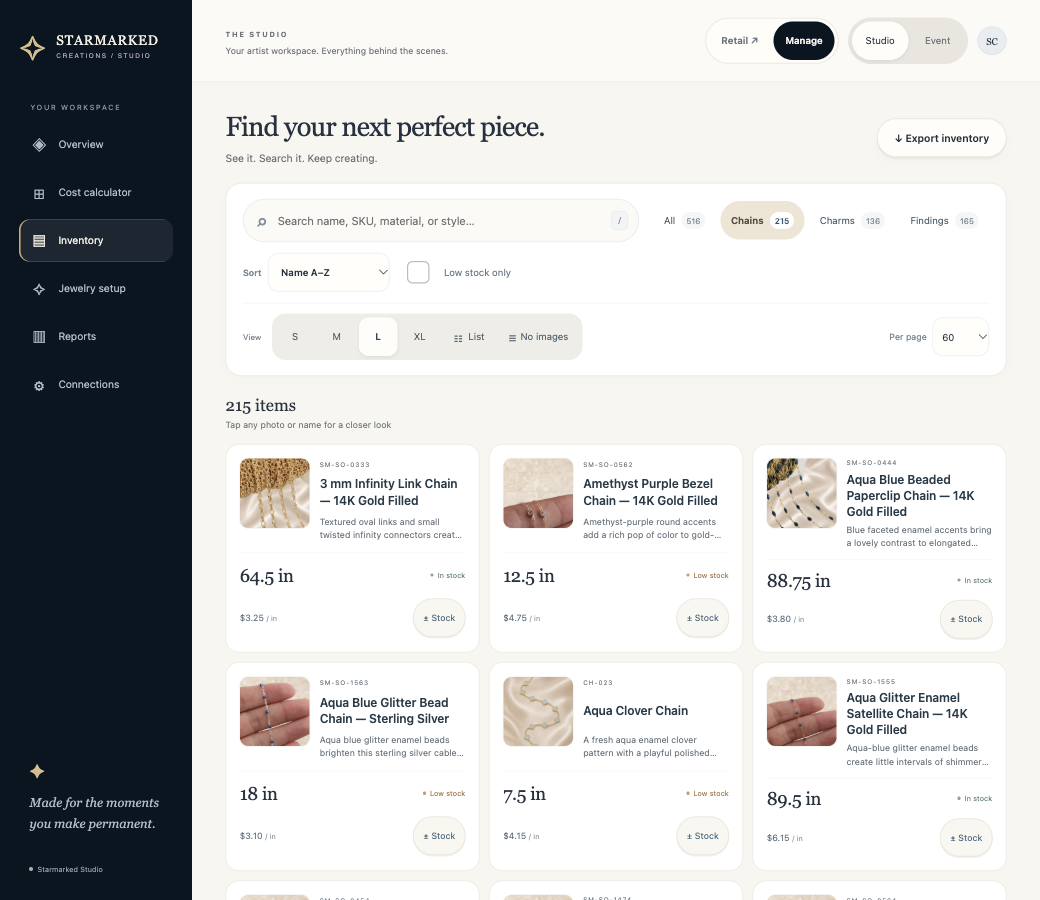
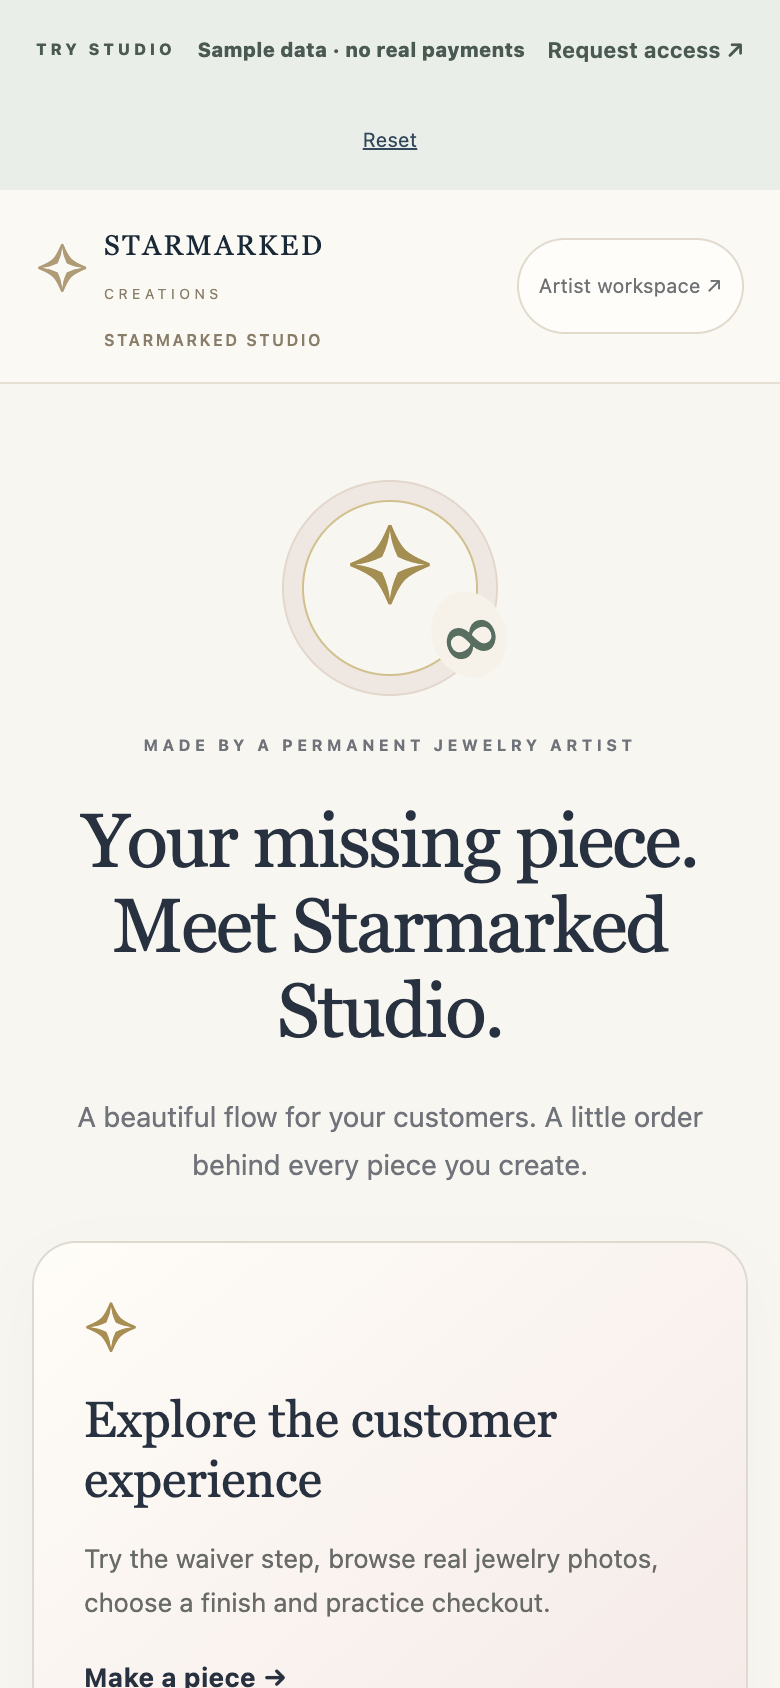
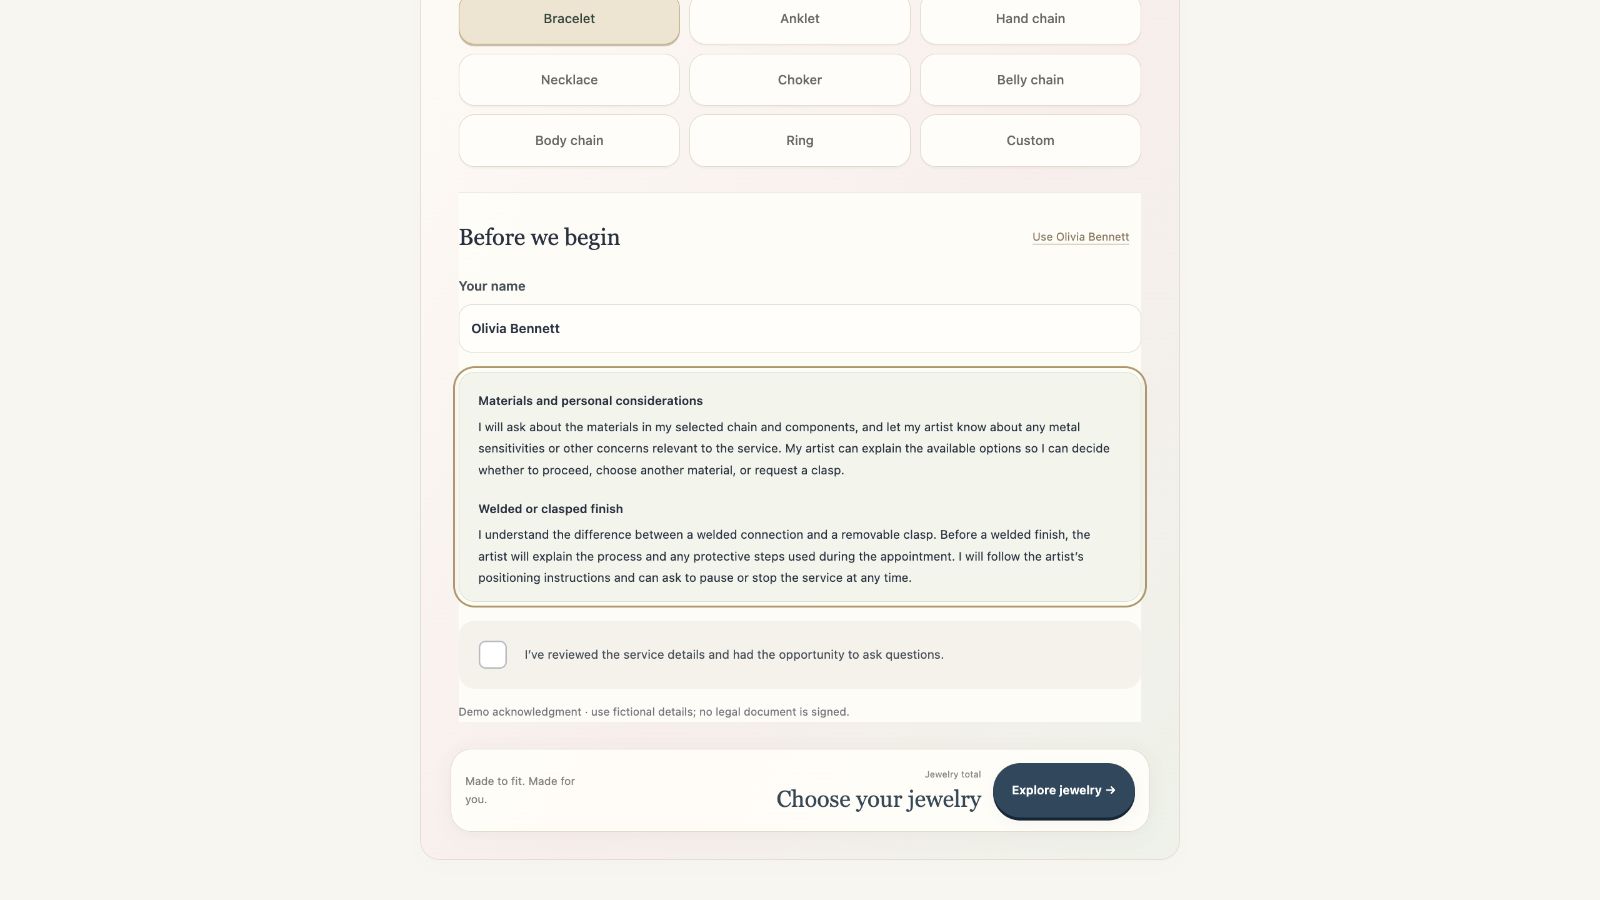
Real Studio screens, presented in illustrative device frames. Select any screen to see the full image.
iMac / Inventory workspaceInventory, product images and stock at a glance.
iPad / Inventory at the counterA visual catalog that supports the conversation.
iPhone / Studio mobile previewA customer-facing starting point on a smaller screen.
Laptop / Customer flowA guided step before choosing a piece.
Built by DanieleLabs
Starmarked Studio
A focused example of our approach: build software around the work a business needs to get done.
01 / InventoryKnow what’s available.
02 / CheckoutMake the sale easier.
03 / OperationsKeep the day moving.
The starting point is your business—not a one-size-fits-all feature list.
Less juggling tools. More getting things done.
When spreadsheets, disconnected systems and manual steps start slowing you down, we can build a practical app that fits the way your business runs.
Inventory tools for tracking products, stock and supplies.
Checkout workflows connected to your chosen payment tools.
Simple dashboards and everyday tasks organized in one place.
Start with the problem that costs you the most time. We’ll define a useful first version, agree the scope and price, and build from there.
I’m Christopher Daniele. My background includes 20 years in infrastructure and security, including enterprise vulnerability management.
I bring that experience to owner-run offices: understanding how you work, identifying what deserves attention, and explaining the next steps without burying you in technical language.
You work directly with me, with a written scope and a clear handoff.
Share your team size, the tools you use and what prompted you to reach out. You can start even if you’re unsure which service fits.
02 / AGREE
Know what’s included.
We agree the systems, deliverables, timing and price in writing before the work begins.
03 / ACT
Leave with a useful plan.
Get your findings, any agreed implementation, and a plain-English walkthrough of what has been done and what comes next.
Before we start
A few useful answers.
Which service should I start with?
The Quick Check is a focused first step if you want to understand your everyday security gaps. If you need a tax office security plan or a HIPAA risk analysis, tell me about that requirement so we can scope the appropriate engagement directly.
Does the Quick Check include fixes?
It includes a 90-minute review, a written prioritized fix list and a 30-minute walkthrough. Findings are delivered within five business days after the review and receipt of the required information and access. Configuration work is agreed separately.
What does “from” pricing mean?
It is the starting price for a typical office of the size listed. The number of systems, locations and information flows can affect the work. You receive a written scope and price before committing.
Does this certify my office as compliant?
These services support your compliance work. They are not legal advice or a certification. Your scope identifies the work DanieleLabs performs and the ongoing responsibilities your office retains.
What response does Security Care include?
Email replies within two business days. That is a response timeframe; the time needed to resolve a request depends on the issue and agreed scope. Monitoring and incident-response needs should be discussed explicitly before enrollment.
Let’s talk security
Tell me about your office.
Share what you’re trying to protect, improve or prepare for. I’ll help you identify the right starting point.
What happens next
I’ll review your request and follow up about your office and the work you need. We agree the scope and price before scheduling a paid engagement.
Keep the first message simple.
Your business type, team size and main concern are enough. Please leave passwords, tax records and patient information out of this form.